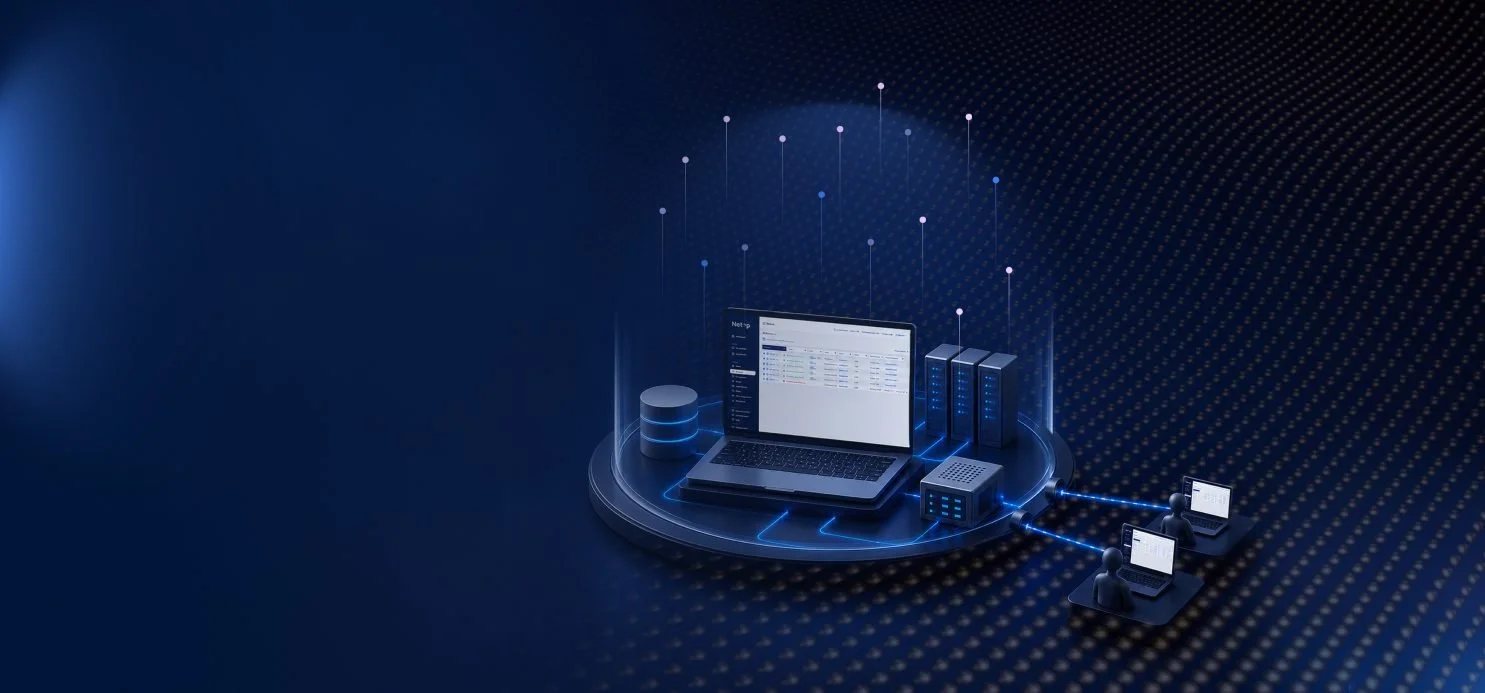
The Netop Portal. Hosted in your environment.
Run controlled, auditable remote operations within your own infrastructure, with full control over deployment, data, and access.
Where traditional remote access falls short
Most remote access solutions are built for convenience, not sovereignty. For organisations operating in classified, air-gapped, or restricted environments, this creates a structural gap that standard workarounds cannot close.
Legacy Infrastructure
Jump boxes, bastion hosts, and legacy remote access appliances predate modern Zero Trust. They often lack the granular controls, visibility, and auditability required under CMMC, NIST 800-171, and IEC 62443.
VPN and third-party access
Extending VPN credentials to third-party vendors can create persistent access, overprivileged accounts, and audit findings that resurface during penetration tests and compliance reviews.
On-site intervention
When remote access cannot meet classification or security requirements, organisations are forced back to physical site visits, adding cost and days of delay across distributed environments.
Netop Self-Hosted Portal: Sovereign by Architecture
The Self-Hosted Portal is designed for defence and government agencies, critical infrastructure operators, and regulated enterprises where vendor-hosted SaaS platforms and cloud-dependent tooling create structural conflicts with classification requirements, compliance mandates, or operational security policy.
-
Deployed entirely on-premise or within a private cloud. No external dependencies: operational in classified, air-gapped, and sovereignty-restricted environments without modification or exception.
-
Customer-owned certificates, keys, and storage. Full local audit retention. No data leaves the infrastructure boundary under any condition.
-
Fully containerised and infrastructure-agnostic across compute, storage, identity, and networking. Portable without redesign. Consistent security posture, whether deployed on-premise, in a private cloud, or within AWS European Sovereign Cloud and Microsoft Cloud for Sovereignty. The deployment model conforms to organisational requirements — not the other way around.
-
Security is enforced at the architectural level, not bolted on as a compliance layer after the fact. No inbound ports. No IP exposure. Granular access controls and least-privilege enforcement are built into the platform from the ground up, with full auditability at every layer.
-
Specific use cases include organisations subject to CMMC, NIST 800-171, CJIS, or HIPAA, where data residency and infrastructure control are non-negotiable; environments where VPN-based third-party access creates unacceptable audit exposure; and distributed operations where on-site vendor visits are costly and time-consuming.
How the Self-Hosted Portal Works
One Portal experience. A different operating model.
Self-Hosted Portal brings the Netop Portal into customer-controlled infrastructure. The Portal experience, endpoint workflows, access model, and Netop remote access ecosystem remain consistent. What changes is where the Portal runs, how the supporting infrastructure is managed, and where operational data is retained.
What stays consistent
The Netop Portal experience
Device inventory and endpoint management
Secure remote access workflows
User, group, and access controls
Netop Guest, Host, and OnDemand
What changes
The Portal runs within customer-controlled infrastructure
The customer controls the hosting environment
Infrastructure and network access remain under customer control
Identity, certificates, keys, logs, and operational data remain inside the customer environment
Runtime does not rely on Netop's shared cloud environment
Security-by-Design for Regulated Environments
With more than four decades of remote access engineering experience, Netop has been securing and supporting mission-critical environments such as ATMs, kiosks, fuel pumps, thin clients, POS terminals, and industrial endpoints. In fact, Netop has operated in these demanding sectors longer than many of its competitors have existed.
-
No inbound ports. No IP exposure. Security enforced at the architectural level, not added as a compliance overlay. Identity bound at the portal layer, with granular access control and full audit retention under your infrastructure.
-
Unlimited tenants supporting large-scale organisational structures and multi-entity deployments.
-
Least-privilege enforcement with role-based controls mapped to organisational structure and clearance requirements.
-
Architected to support SOC 2, PCI DSS, CJIS, HIPAA, CMMC, and NIST 800-171 requirements.